 小影邮箱
邮件登录提醒要开吗?Alerts You Should Keep On
Key Takeaways
- A 邮件登录提醒 warns you when a new device signs in.
- It is one of the cheapest security settings you can turn on.
- Enable it for every account that holds sensitive mail.
- Read the alert and confirm the device before you relax.
- If it was not you, act within minutes.
What a 邮件登录提醒 catches
A 邮件登录提醒 is a short message after a sign-in. It names the time, the device and often the place.
Its purpose is simple. You learn about a new login while you can still react.
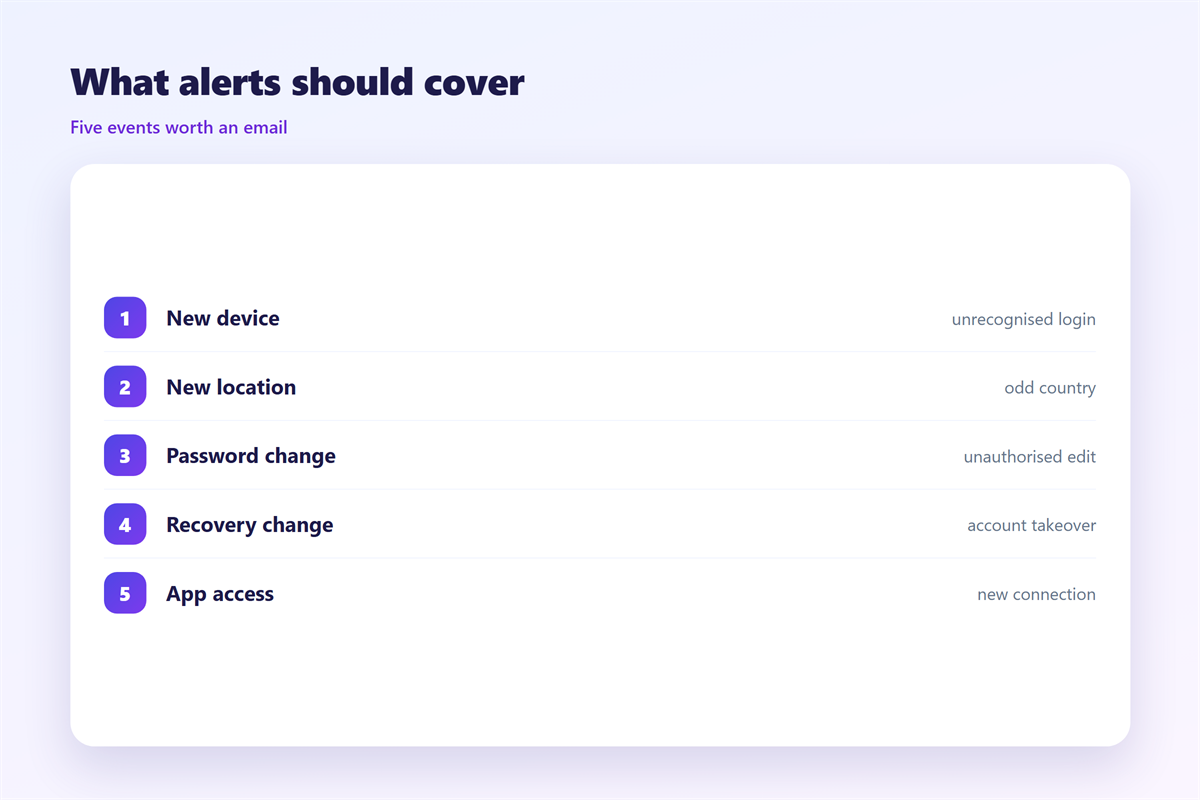
Most alerts fire on a new device or a new location. A routine login on your own laptop stays quiet.
That design keeps the signal useful. You only hear about logins that stand out.
A 邮件登录提醒 also catches password reuse. A login you did not make is proof someone else has the password.
The alert may also mention a blocked attempt. Repeated blocks point to someone guessing.
Some alerts also flag a changed password. That is another sign worth reading.
Some services add a time and an IP address. Both help you judge whether the login was yours.
The alert is not a lock. It informs you, and you decide the next move.
Treat it as a smoke detector. It is quiet on normal days and loud when something is wrong.
Why 邮件登录提醒 matter
Passwords leak in large numbers every year. A stolen password can be used within minutes.
A 邮件登录提醒 shrinks that window. You see the login before the attacker reads much mail.
Email is the key to everything else. A reset link for another site lands in your inbox.
So the inbox deserves the strongest warning. One alert can protect many accounts.
邮件登录提醒 also help after a breach elsewhere. If a reused password was exposed, alerts catch the follow-up.
They cost nothing to enable. That makes them one of the best settings available.
Alerts do not replace a strong password. They work best together with two-factor authentication.
Together they cover both halves. One stops the theft, and the other reveals it.
Reliable alerts make you calmer, not more anxious. You know you will be told.
Attackers often log in quietly and read mail first. The alert interrupts that plan.
Turning on 邮件登录提醒 well
Enable alerts for every serious account. Start with your main email, then expand.
A 邮件登录提醒 should reach a channel you check. Sending the alert to the account itself is weak.
If possible, send it to a second address. That keeps the warning safe when the first account is compromised.
Turn on alerts for the recovery address too. It is a common target.
Check the settings after a provider update. Options sometimes move or reset.
Test the alert once. Trigger a login from a new device and confirm the message arrives.
Choose alerts for new devices over every login. Constant warnings get ignored.
Review the recipients each year. An old phone number may no longer reach you.
Choose the strongest channel you actually read. A missed alert is no alert.
A working 邮件登录提醒 is verified, not assumed.
Reading a 邮件登录提醒
A real alert is calm and factual. It names a device, a time and a place.
Read it slowly before you panic. Phishing mail copies the look of real alerts.
Check the sender address carefully. The mail should come from the service you use.
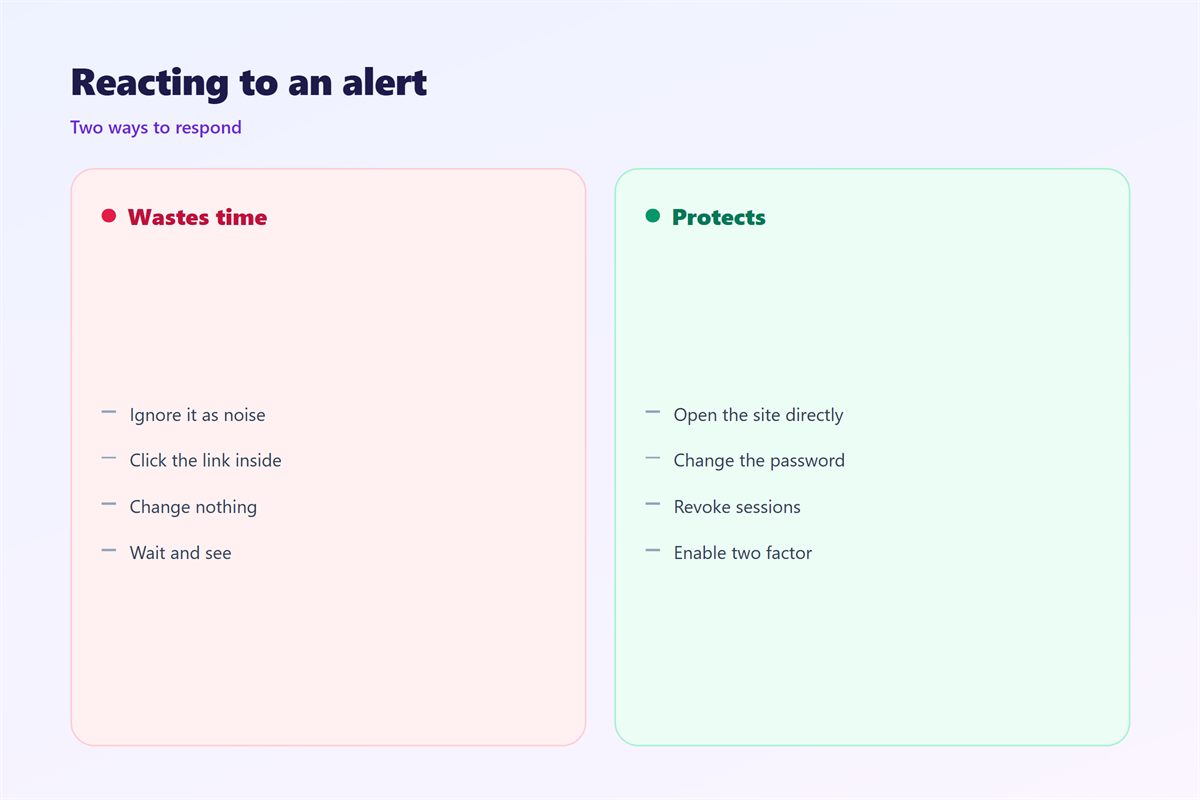
Do not click links inside an unexpected alert. Open the app or site yourself instead.
A 邮件登录提醒 that pressures you is suspect. Real alerts do not demand an instant password change.
Look at the device name. “Unknown device” deserves a closer look.
Compare the location with your day. A login from another country rarely fits.
The time matters too. A login at three in the morning is worth a check.
Keep the alert for later if unsure. You can always check it again.
When the details match your own activity, close it. When they do not, act at once.
What to do after a 邮件登录提醒
A strange alert needs a fast, ordered response. Panic wastes the minutes that matter.
Change the password first. Do it from a device you trust.
Sign out other sessions if the option exists. That ends a thief’s access right away.
Turn on two-factor authentication. It blocks the next attempt even if the password leaks again.
Check the account recovery settings. An attacker often adds a new recovery address.
A 邮件登录提醒 that fires again proves the first fix was incomplete.
Review recent mail for hidden rules. Forwarding rules are a common trick.
Tell your contacts if strange mail went out. A warning limits the fallout.
Change reused passwords on other sites. The attacker will try the same password elsewhere.
Write the new password down in a manager. Losing it locks you out too.
Tell your IT team if the account is shared. They can watch for more attempts.
Keep the alert switched on afterwards. The warning system is now your ally.
Our guide to 邮箱安全 covers the full hardening routine. Unusual sign-in signals are described under 邮箱登录异常. Which alerts to keep sits in 邮件通知, and the breach response lives under 邮箱泄露.
FAQ
Should I keep 邮件登录提醒 on every account?
Yes for important accounts. Start with email and finance, then add the rest.
Are 邮件登录提醒 ever fake?
Yes. Phishers copy them to make you click. Check the sender and open the app yourself.
Is an alert enough without two-factor authentication?
No. Alerts inform you, while two-factor blocks the login. Use both together.
An alert fired for my own login. Should I worry?
Usually not. If the device and time are yours, no action is needed.
评论
还没有评论,来说两句吧。
评论功能已关闭。