 小影邮箱
邮件防篡改怎么看?Spot a Changed Message
Key Takeaways
- 邮件防篡改 is about spotting a message that changed.
- A swapped link is the most common warning sign.
- A forged sender often hides behind a lookalike address.
- Check the raw headers, not just the friendly name.
- A signed message makes tampering far harder.
What 邮件防篡改 means
邮件防篡改 starts with a question. Did this message arrive the way it was sent?
Mail travels through many servers. Any one of them could alter it.
In practice most tampering is simple. A link is swapped for a fake one.
So real protection means checking, not trusting. Look before you click.
Two tools do the heavy lifting. A signature and careful header reading.
The goal is simple. You want the same text the sender wrote.
Most 邮件防篡改 work happens in a few seconds of checking.
A plain message carries no lock. Anyone on the path can read or edit it.
Most alterations target the link, not the words. People click without looking.
A few changes can hide in plain sight. Only a careful reader notices them.
So the work is really about habits, not clever tools.
Why 邮件防篡改 matters
One changed link can drain an account. The rest of the message looks normal.
One wrong click can cost real money. A moment of doubt is cheaper.
The habit also builds a calmer team. People stop panicking after every mail.
Spam filters catch some fakes but not all. Human eyes still matter.
How 邮件防篡改 catches a fake
A signature that fails is a loud warning. Stop and check by another route.
A link that does not match its display text is another red flag.
Good 邮件防篡改 habits are cheap and quick to learn.
It protects the quiet reader too
Busy people click fast. A habit of checking protects them on a bad day.
Teams that check together report fewer successful attacks.
How to spot a changed message
Hover over a link before you click it. Read where it really goes.
A mismatch between text and target is a strong signal. Slow down.
Look at the full address, not just the name. A single letter can differ.
Watch for odd wording or a sudden urgency. Pressure is a common trick.
Reading the raw headers is part of 邮件防篡改. The server path tells a story.
Compare the reply address with the sender. A gap is worth a second look.
Never open an unexpected attachment at once. Confirm it first by phone.
That is 邮件防篡改 practice in daily life, one message at a time.
Look for a greeting that feels off. A strange tone can signal a fake.
Check the time a message arrived. Odd hours are sometimes a clue.
Notice the sender’s domain, not just the display name. One letter matters.
If two signals appear at once, stop and verify. Two flags are a pattern.
A calm reader spots more than a rushed one. Slow down once.
Where 邮件防篡改 tools help
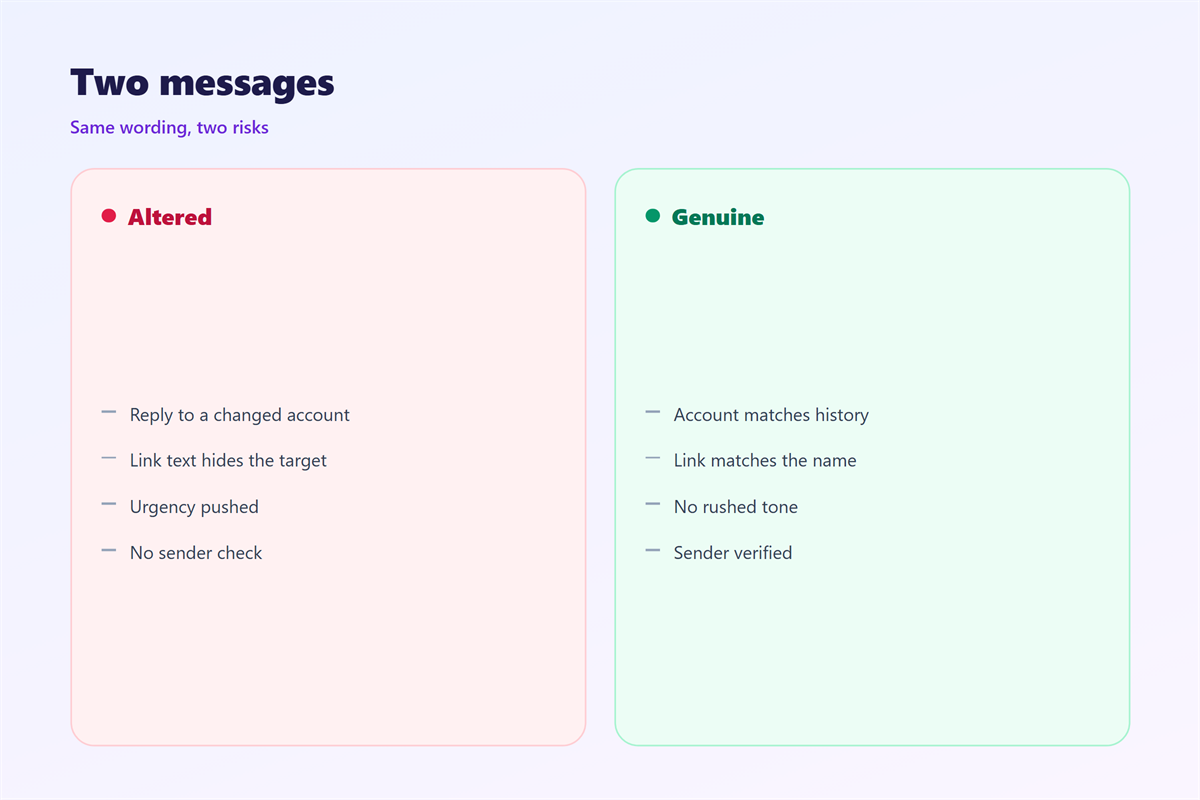
A signed message is the strongest single defence. Learn to read the badge.
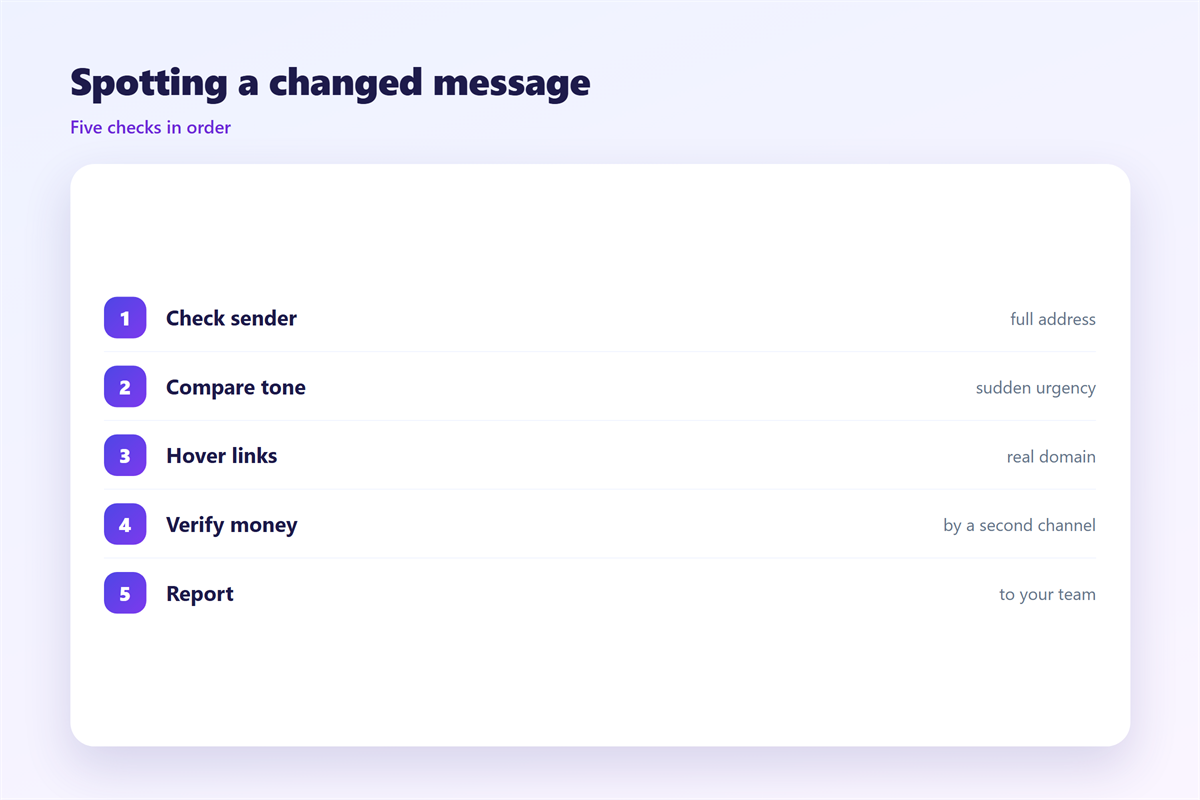
A valid signature means the text arrived intact. A missing one proves nothing.
Header checks catch the rest. The first server line is often the key.
Keep a clear record of what arrived. It helps after a real incident.
Store the raw 邮件防篡改 evidence safely. A later review may need it.
Automated rules can flag risky mail. They reduce the load on tired eyes.
Still, a human check catches what rules miss. Keep both in play.
Keep your mail client up to date. Newer versions flag more risks.
A second channel confirms a real request. A quick call settles doubt.
A short report of a fake mail helps everyone. Share what you found.
Every extra check adds a little safety. Keep the steps short.
Common mistakes
The first 邮件防篡改 mistake is trusting the display name.
The second is clicking before hovering. One second of care blocks most tricks.
The third is ignoring a failed signature. That failure is the whole point.
Another 邮件防篡改 mistake is deleting the original. Keep it for review.
Do not rely on the padlock alone. It covers the link, not the sender.
Do not forward a suspect mail. You may spread the problem.
Do not judge a message only by its logo. Logos are easy to copy.
Do not skip the check because you are busy. Busy is when errors happen.
Building a simple checking habit
Slow down on any message that asks for money or a login.
Hover every link in a mail you did not expect. It takes a moment.
A quick second check beats a costly cleanup later.
Teach the habit to your team. Shared checks catch shared threats.
A 邮件防篡改 routine is only useful if you run it every day.
A shared 邮件防篡改 habit protects the whole team at once.
Log what you find. A short record helps the next review.
Practice the same order every time. A fixed routine is hard to forget.
Share examples with new staff. Real samples teach faster than rules.
Review one real case each month. Learning sticks when it is real.
Our guides make the pieces clearer. Read up on 邮件冒充 to spot a forged sender, and keep an 邮件审计 trail of what arrived. Learn to read the raw 邮件头, and understand the 邮件证书 behind a valid signature.
Together these habits close most of the gap.
FAQ
Can 邮件防篡改 stop every attack?
No method is perfect. It raises the cost and catches most changes.
How do I check a link safely?
Hover over it, or copy the target into a plain text editor first.
What is the clearest sign of tampering?
A failed signature, or a link that does not match its display text.
Do I need special software?
Most clients show a signature badge already. No extra tool is required.
评论
还没有评论,来说两句吧。
评论功能已关闭。