 小影邮箱
邮件MTA-STS 怎么配?Enforce Secure Delivery
Key Takeaways
- 邮件MTA-STS forces encrypted mail delivery.
- It closes a gap that plain transport leaves open.
- A published policy tells senders what you expect.
- Reports show who still ignores it.
- Testing first avoids broken deliveries.
What 邮件MTA-STS means
邮件MTA-STS is a policy that demands encrypted delivery between servers.
Without it, mail can travel in the clear on the open internet.
The policy lives in two places. One is a DNS record, the other is a file.
邮件MTA-STS stands for Mail Transfer Agent Strict Transport Security.
The long name explains the job. It keeps transfer agents on a secure path.
If a server cannot encrypt, the policy tells your mail server to stop.
So 邮件MTA-STS turns a hope for privacy into a hard rule.
The rule applies between servers, not on the reader’s screen.
It works quietly, with no change for the person receiving the mail.
It sits between two mail servers during transfer.
No one has to install anything on a phone.
It simply sets the rules for the connection.
Mail that cannot meet the rules waits or fails.
That clear behaviour is what makes it useful.
It works with the normal mail flow.
No extra step is added for senders.
It is invisible when everything works.
Why 邮件MTA-STS matters
Mail crosses many networks before it arrives. Each hop is a chance to peek.
A downgrade attack can strip encryption mid trip. The policy blocks that trick.
A firm 邮件MTA-STS also reassures partners. They know you take security seriously.
It protects both sides of the conversation, not just one.
Regulated industries often expect this level of care.
A silent downgrade is easy to miss.
Most people would never notice it happening.
The policy removes that quiet risk.
It also shows auditors that you are serious.
It closes a common, quiet gap.
Small steps like this add real safety.
That quiet work is exactly the point.
Reading 邮件MTA-STS reports
Reports list servers that tried to deliver without encryption.
Use them to fix partners instead of guessing who is at fault.
Watch the reports each week while the policy is new.
Too many failures often mean a missing host.
Read the report with the sender before you worry.
What 邮件MTA-STS covers
It covers the path between mail servers while mail moves.
It does not encrypt the message once it is stored.
It also does not replace a signature that proves the sender.
It only guards the trip, not the mailbox.
The message itself is still stored in plain form.
How to set up 邮件MTA-STS
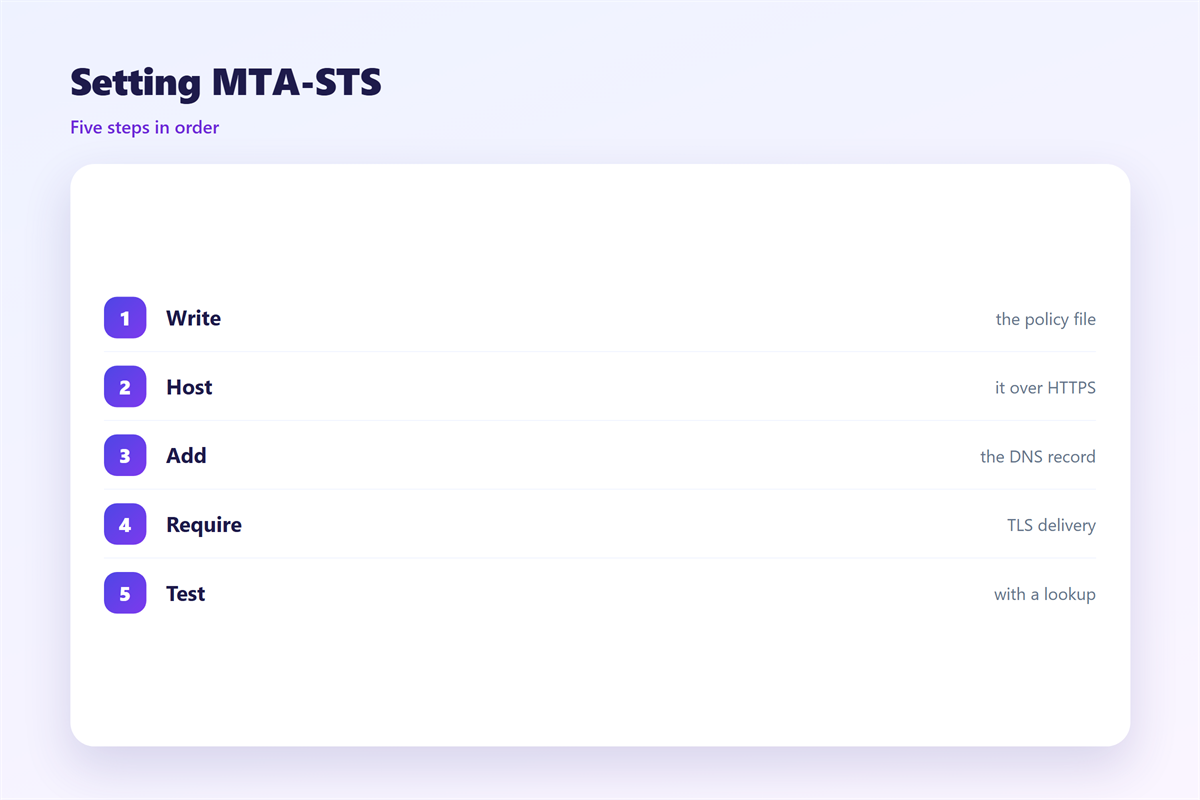
Start with a test mode so nothing breaks during setup.
Publish a DNS record that points to your policy file.
Host that policy file on a secure web address.
List the hosts that are allowed to receive your mail.
Add a reporting address to collect delivery feedback.
Watch the reports for a few weeks before you enforce the rule.
Then switch the policy from testing to enforcing.
A careful 邮件MTA-STS rollout rarely surprises the team.
Keep the policy file short, with one clear version number.
Set a sensible time to live on the DNS record.
Tell partners before you enforce, so they can prepare.
Save a copy of every version of the policy file.
Start the policy with a low number so testing is safe.
Raise the number only when the reports look clean.
Keep the wording of the file simple and clear.
List every host that receives mail for you.
Double check the host names before enforcing.
Ask a partner to send a test message.
Keep the file tidy and easy to edit.
Store the current version in one place.
Measuring 邮件MTA-STS
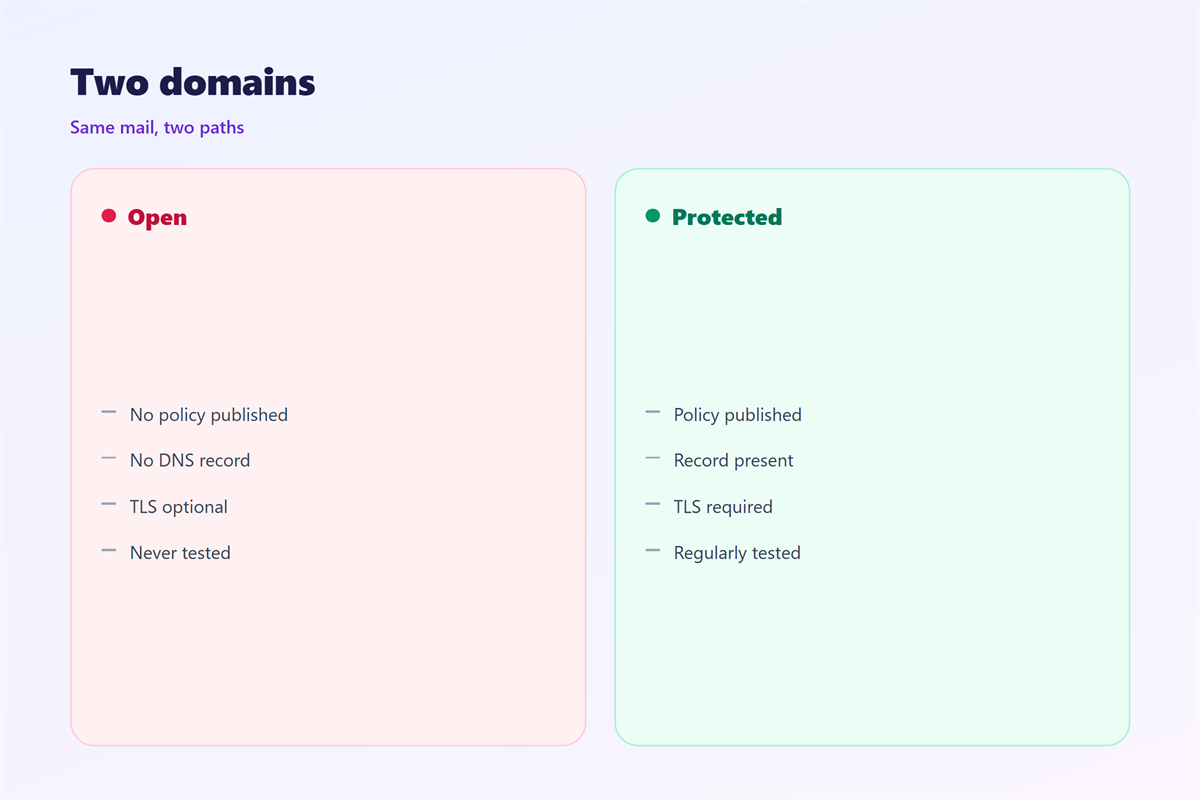
Check that the policy file loads over a secure connection.
Confirm the DNS record resolves for every sender.
Review the reports for repeated failures.
Keep the policy simple and easy to read.
Test 邮件MTA-STS again after every change.
Look for hosts that keep failing and fix them one by one.
Record the date of each change to the policy file.
Update the file whenever your mail hosts change.
Do a quick check after any provider migration.
Compare the reports week by week during testing.
Watch the failure count fall as you fix hosts.
Note the exact date you switch to enforcing.
Check the policy after any change to your website.
Alert the team if the failure count jumps.
A sudden jump usually means a missing host.
Sending and improving
Point the policy at the right hosts. The basics sit in 邮件MX记录.
Understand what each layer protects. The layers are in 邮件加密.
Prove who is sending the mail. The proofs sit in 邮件认证.
Keep the transfer channel open. The settings are in 邮件端口.
Then check 邮件MTA-STS again after each release.
Steady checks keep the policy working all year.
Write the policy rules in plain words for the team.
Keep a copy of the recent reports on file.
Review the setup with the team once a year.
Then enjoy quieter, safer mail.
Safe delivery protects the whole brand.
A routine check keeps it that way.
FAQ
Does 邮件MTA-STS encrypt the message content?
No. It protects mail in transit between servers, not at rest.
Do I need a policy file and a DNS record?
Yes. Both are needed for the standard to work.
What happens if a server cannot encrypt?
In enforce mode, the message is not delivered. The sender is told why.
Is testing mode safe to run?
Yes. It reports problems without blocking any mail.
评论
还没有评论,来说两句吧。
评论功能已关闭。