 小影邮箱
邮件白名单怎么设?Where It Helps and Where It Leaks
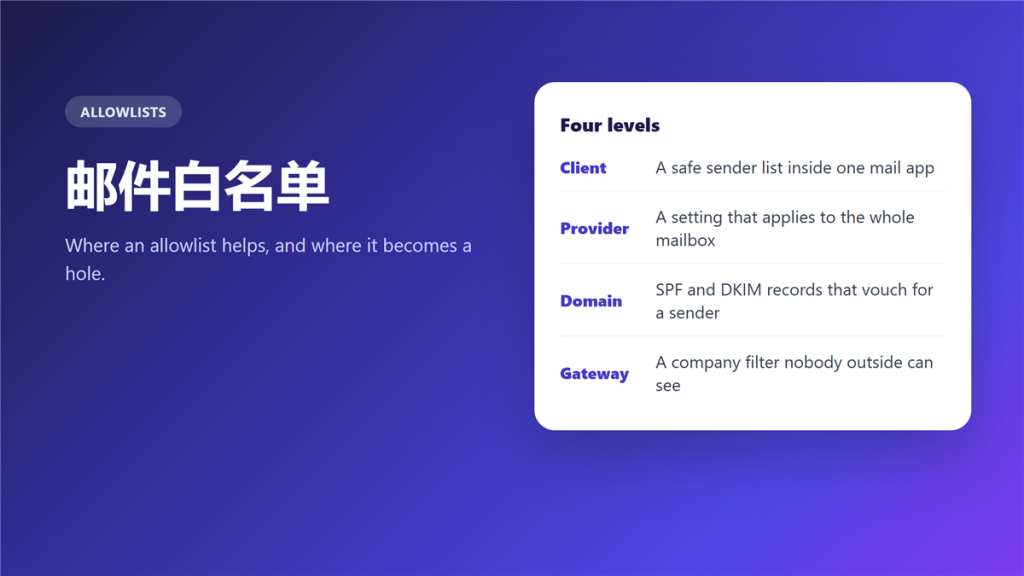
What a 邮件白名单 can and cannot do
邮件白名单 is a promise you make to your own filter: this sender is allowed through. It works, and it works narrowly, because a filter decides on far more than sender identity.
A support team added a client domain to their list and still lost two weeks of tickets. The mail had passed the sender check and then failed a different rule entirely. The 邮件白名单 had done its job perfectly, and the problem was somewhere else.
Key Takeaways
- 邮件白名单 covers senders, not content.
- Five levels of allowlist exist, and only two are really yours.
- An allowlist never overrides a virus filter.
- Contacts bypass filters more often than people realise.
- A wrong entry is how impersonation succeeds.
- Test the entry before you rely on it.
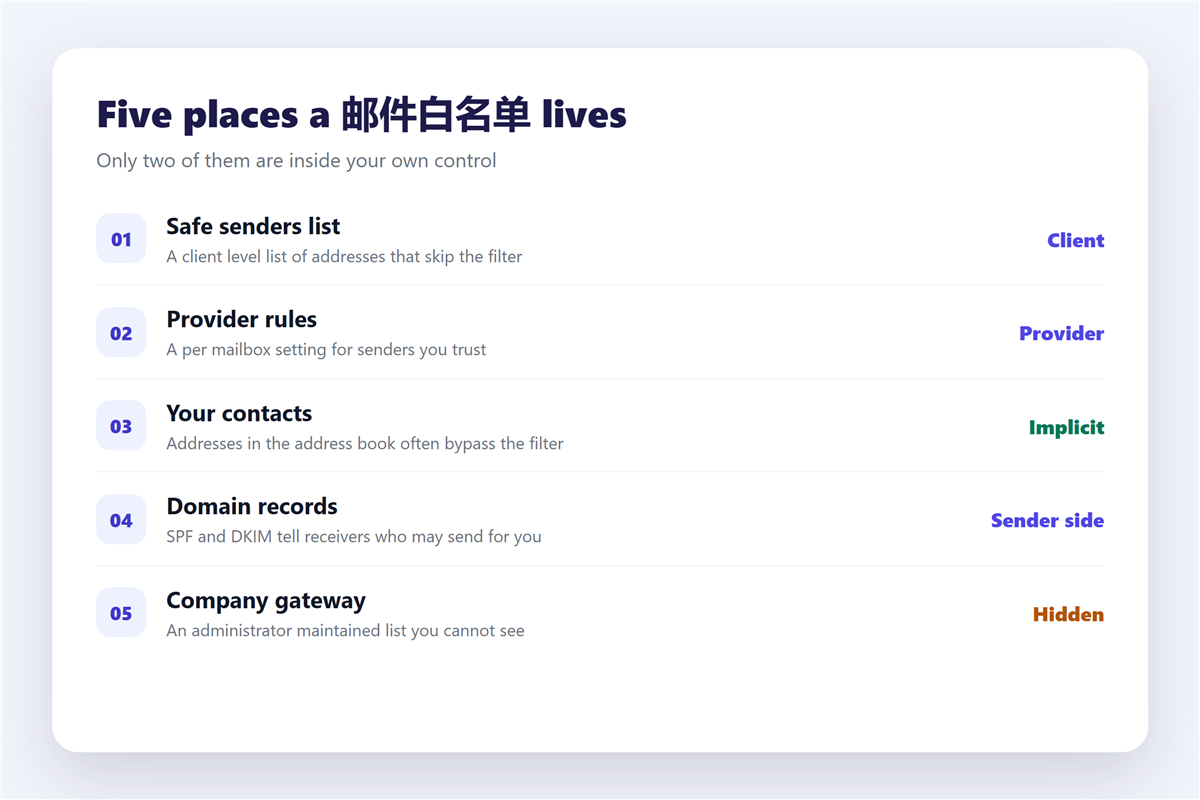
Five places a 邮件白名单 lives
- The safe senders list inside one mail client.
- A provider level rule that covers the whole mailbox.
- The address book, which many filters consult implicitly.
- DNS records that authorise a sender before delivery even starts.
- A company gateway list, maintained by an administrator you may never meet.
The second level is the one most people can actually change, and the fifth causes the most confusion. Because a gateway sits upstream of everything else, a message it rejects never reaches your rules at all. The reverse case, where a legitimate sender is wrongly blocked, is diagnosed in 邮件误判.
When a 邮件白名单 helps most
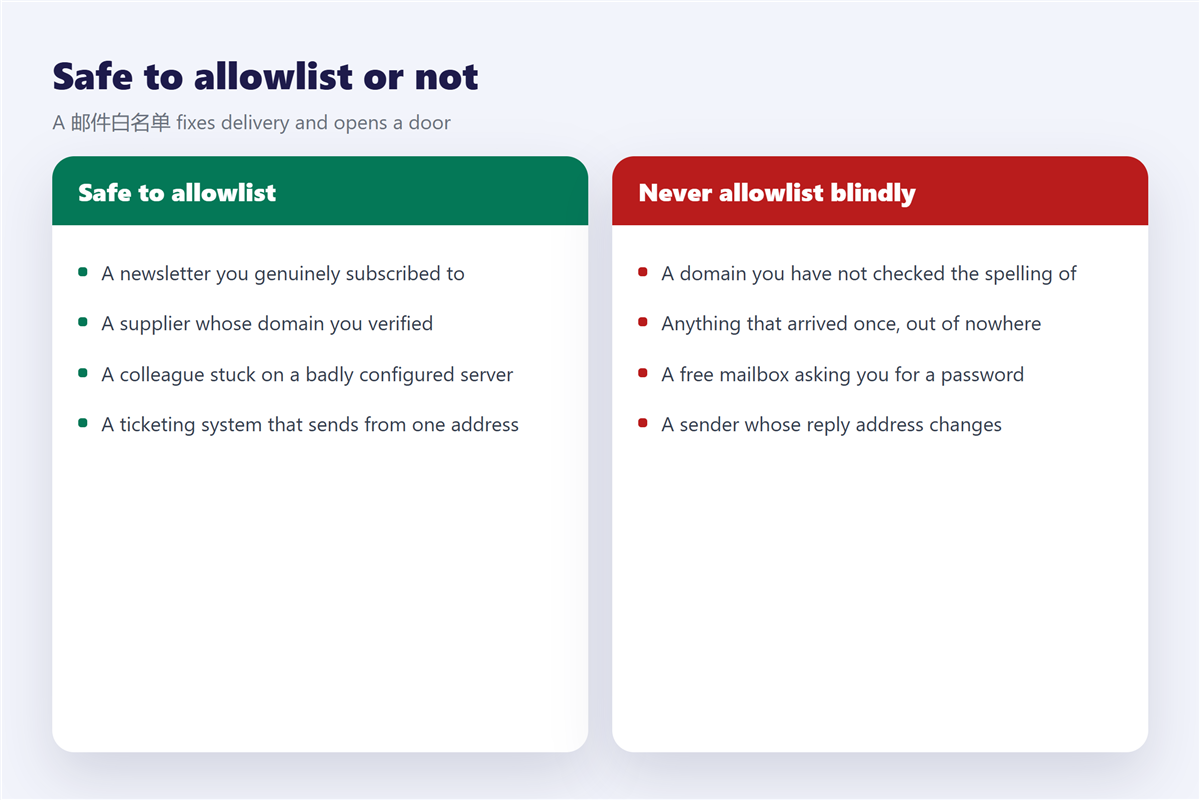
Three situations justify an entry, and each one has a clear test.
A newsletter you subscribed to but stopped receiving is the simplest case, because the sender is known and the content is expected. A colleague stuck on a badly configured server is the second, and it is worth confirming that the domain is really theirs first. The third is a machine that sends from a single fixed address, such as a ticketing system. The sender side of the same problem, where your own mail is being refused, is covered in 邮件黑名单.
When an allowlist becomes a hole
Every entry you add is a sender that will reach you without further checking, which is exactly what an attacker wants.
A domain one character away from a supplier is the classic trick, and it is invisible once it sits in a list. Furthermore, a list rarely survives the case where a trusted account was compromised, so mail from a real supplier address can still be hostile. That risk is why attachments deserve their own check whoever sent them, and the workflow is in 邮件附件. The signs that a sender is not what it claims are laid out in 钓鱼邮件.
How to test an entry before you rely on it
- Write down the exact domain, not just the display name.
- Send yourself a message from that domain and watch where it lands.
- Remove the entry once the problem is solved, and see whether the mail still arrives.
- Review the whole list twice a year and delete anything you cannot justify.
The third step is the one people skip. Notably, an allowlist that is never pruned stops being a decision and becomes an accident. For the wider picture of where unwanted mail originates, see 垃圾邮件.
Frequently asked questions
Does a 邮件白名单 override the spam filter?
For that sender, usually yes. It rarely overrides a virus or attachment filter, which is deliberate.
Can a 邮件白名单 be set by the sender?
No. A sender can only publish records that help; the list itself always belongs to the receiver.
Why does my 邮件白名单 not work?
Usually because an upstream gateway rejects the message before your rules see it, or because a second rule moves it straight afterwards.
Is a 邮件白名单 the same as marking mail as not spam?
Related, not identical. Marking a message trains the filter over time, and a list entry overrides it for one sender.
评论
还没有评论,来说两句吧。以下为本文的引用通告: